Quality Management Services


Audit Quality Advisory Services for Accounting Firms
Quality Management Services

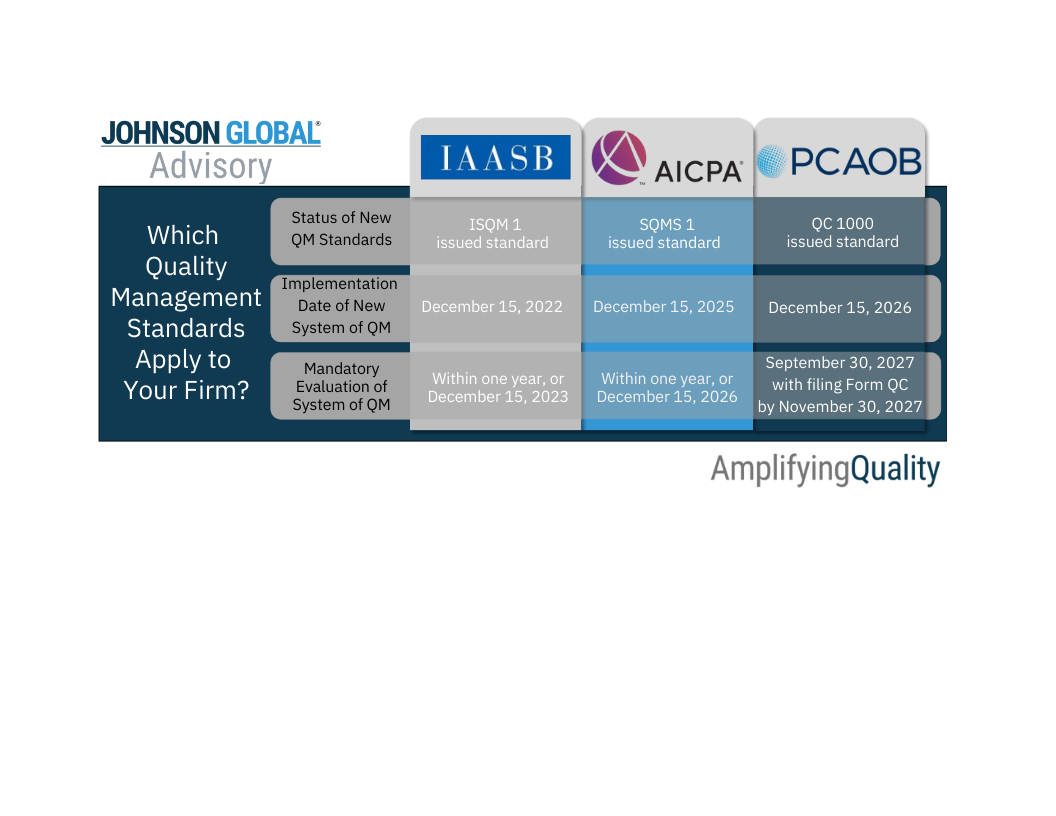
Quality management is a critical component for firms of all audit practices, including issuer and broker-dealer audits. Firms are required to comply with quality management and quality control standards related to their system of quality management. Specifically, the IAASB, AICPA, and PCAOB have adopted ISQM 1, SQMS 1, and QC 1000, respectively. As a result, firms that are required to follow IAASB, AICPA or PCAOB standards need to reconsider their quality management systems and implement policies and procedures to comply with these requirements.


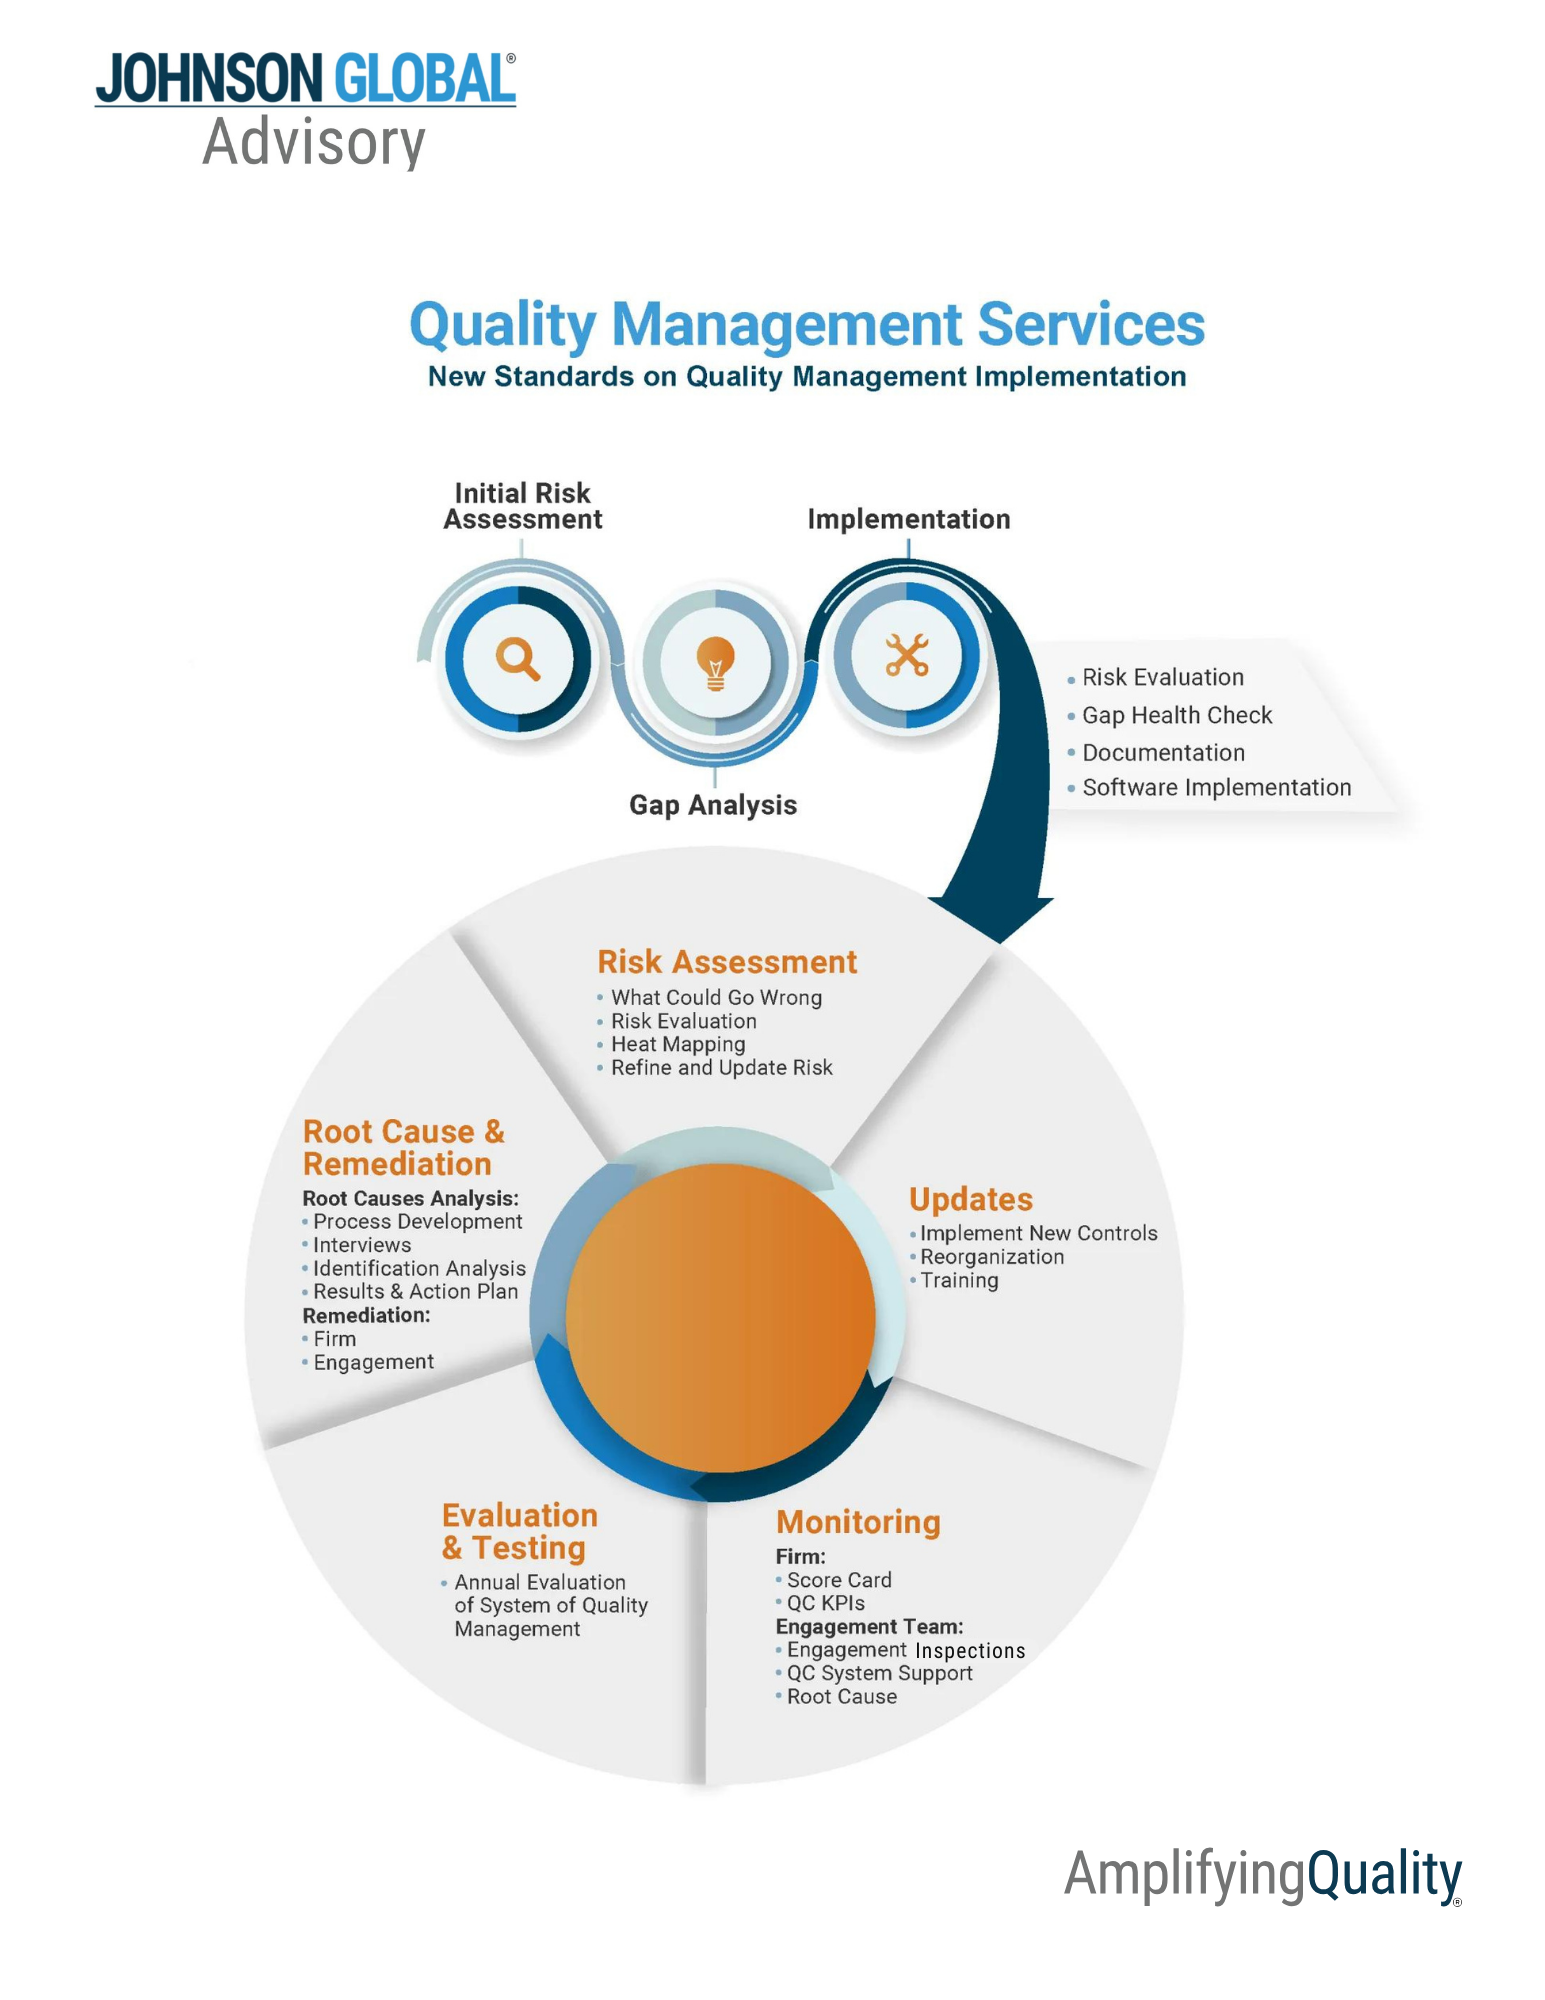
The following diagrams depicts the steps that a firm should undertake to initially adopt and implement the quality management standards and the iterative and cyclical nature of operating their system of quality management on an annual basis:
Through our experiences evaluating systems of quality control at firms that operate domestically and internationally and completing hundreds of firm inspections, we as Advisors, meet firms where they are and understand the significant effort and the changes required by firms to implement and operate their system of quality management under the new quality management framework. These required changes will affect firms around the globe due to the amount of effort involved given the rigor of these standards. 


We have supported firms' initiatives to establish the appropriate policies, processes and systems to address the changes required in the adoption of the quality management standards. These changes include developing a robust risk assessment process, establishing governance and leadership controls, expanding firm policies and controls around independence and ethics requirements, and identifying and establishing appropriate policies and controls for firm technological, intellectual, and human resources. This work also includes developing or improving processes and controls over monitoring and remediation, including root cause analyses.


JGA has the experience and the team to help firms implement and operate their system of quality management and comply with the quality management standards.
Our Services Include:

Risk Assessment


  • Identify the “what could go wrongs” 
  • Perform a risk evaluation 
  • Assist or perform risk heat mapping development and implementation 
  • Refine and update risks 

Implementation and Training


  • Assist with new or revised control implementation 
  • Support reorganization/realignment 
  • Develop, deliver, and consult on training programs 

Monitoring


  • At firm level 
  • Develop and implement score cards and QC KPIs 
  • At engagement level 
  • Perform pre- and post-inspections 
  • Perform root cause analysis, including
  • interviews with engagement teams 

Evaluation and Testing


  • Assist with the annual evaluation of the system of Quality Management including development, implementation and evaluation 

Quality Management Readiness 


  • Perform an initial risk assessment 
  • Perform a gap health check on key components of the firm’s QC process 
  • Support QC documentation efforts 
  • Advise on software implementation 
  • Refine and assist with developing QC processes 

Root Cause and Remediation 


  • Root Cause 
  • Assist with methodology / audit tool development 
  • Conduct interviews 
  • Perform and analysis of root cause findings 
  • Complete and report on root cause analysis 
  • Remediation 
  • Design and execute on remedial action plans for firm-level deficiencies 
  • Assist with engagement level remediation and resolution
March 30, 2026
In a previous article, Back to Basics: Audit Documentation Failures Have Become Dangerous Low Hanging Fruit , we highlighted how audit documentation had quietly re-emerged as a source of regulatory risk after years of relative deprioritization. While PCAOB Auditing Standard 1215, Audit Documentation (AS 1215), has historically been cited less frequently than other standards, our direct experience from recent inspection activity, enforcement actions, and internal inspection results, demonstrate that documentation failures are increasingly treated as indicators of deeper execution, supervision, and quality management breakdowns. In today’s environment, audit documentation is no longer merely a record of work performed. It is the primary evidence inspectors rely on to evaluate whether an engagement was properly planned, executed, and supported at the time the auditor’s report was issued. What has been low-hanging fruit now requires firms to close these gaps and transform them into a load-bearing foundation for audit quality. From Rare Enforcement to Systemic Inspection Risk AS 1215 establishes clear requirements regarding what must be documented, when documentation must be completed, and how engagement files must be assembled and retained. As discussed in our prior article, failures to comply with these requirements were historically viewed as technical or secondary issues, often resulting in inspection comments rather than enforcement action. That distinction is no longer meaningful. Recent enforcement actions involving backdating, improper (both intentionally, and inadvertent) modification of workpapers, and failure to timely assemble a complete audit file reflect an evolving regulatory view. Documentation failures do not simply violate procedural requirements; they call into question the credibility of the audit opinion itself. More importantly, beyond enforcement, documentation deficiencies are increasingly cited as core inspection findings. Inspectors are challenging situations where engagement teams assert that work was performed but cannot demonstrate that work within the archived file. In these cases, the absence of timely, complete, and clear documentation is no longer treated as a formality. It is treated as evidence that the engagement may not have been properly executed, supervised, or supported in accordance with PCAOB standards. This represents a fundamental shift. Documentation is no longer “low-hanging fruit.” It is a systemic inspection risk that cuts across execution, supervision, and firm-level quality management. From Misconduct to Execution Failures Pervasive documentation failures that do not involve intentional misconduct but still result in non-compliance are increasingly observed. For example, reviewer signoffs occurring near the documentation completion date, rather than contemporaneously with the performance of audit procedures, raise questions about whether effective supervision occurred during the audit or was deferred to meeting archiving deadlines. Similarly, engagement teams may assert that key judgments can be explained verbally, even when those judgments are not clearly documented in the audit file. In today’s environment, the distinction between “we can explain it” and “it is clearly documented” is critical. If procedures, judgments, and conclusions are not evident in the documentation itself, inspectors increasingly conclude that the work was not performed in accordance with PCAOB standards. The issue is not whether the engagement team can explain what they did after the fact. The issue is whether the archived documentation allows an experienced auditor, with no prior connection to the engagement, to understand the procedures performed, evidence obtained, and conclusions reached at the time of the auditor’s report. When documentation fails to reach that standard, inspectors are increasingly concluding that the audit itself was not properly executed, regardless of intent. This reflects an important shift. Documentation failures are no longer viewed primarily as misconduct. They are viewed as symptoms of execution breakdowns, including delayed supervision, compressed review cycles, and audit workflows that defer documentation until the end of the engagement. As a result, AS 1215 has become a direct proxy for how audits are actually performed in practice. How the 14-Day Documentation Completion Requirement Changes the Risk Profile The execution risks are further amplified by the PCAOB’s shortened documentation completion timeline. Recent amendments to AS 1215 reduce the timeframe to assemble a complete and final audit file from 45 days to 14 days after the report release date. While this change may appear procedural, its implications are operational. Under this accelerated timeline, engagement teams no longer have a meaningful post-issuance window to resolve review notes, complete documentation, or finalize supervisory evidence. What were once viewed as “clean-up” activities are now more likely to result in timing violations and non-compliance. This shift places increased emphasis on: Contemporaneous documentation Real-time supervision Realistic workload and staffing models Audit Documentation as a Cornerstone of Audit Quality Audit documentation has long been described as low-hanging fruit in the inspection process. That characterization no longer reflects its role in today’s regulatory environment. Documentation now serves as the primary lens through which regulators assess whether an engagement was properly executed, supervised, and supported. With shortened timelines, expanded quality management expectations, and increased regulatory scrutiny, firms can no longer treat documentation as a downstream activity. It must be embedded into how engagements are planned, staffed, reviewed, and completed. In an environment where inspection conclusions are driven by what is, and what is not, in the audit file, strong documentation is not merely defensive. It is foundational to audit quality. At Johnson Global Advisory , we support firms in selecting, implementing, and optimizing these tools to meet their unique needs. For more insights, visit our blog or contact us to learn how we can help your firm AmplifyQuality®. For more information, please contact your JGA audit quality expert .
January 20, 2026
Introduction The accounting firm industry experienced a ground-breaking transaction in August of 2021 when TowerBrook acquired EisnerAmper, which marked the first private equity (“PE”) transaction of a large-scale accounting firm. This transaction was structured using an alternative practice structure (“APS”). Historically, licensing and independence rules have barred non-CPAs from owning accounting firms. Through an APS, a PE firm may invest in the non-attest entity with service lines such as tax advisory and consulting. The CPA partners retain control over the attest functions, which preserves regulatory compliance. While the APS model has been in existence since the 1990s, this August 2021 transaction brought new attention to this structure. What has followed is an extraordinary volume of deal activity. Per the CPA Trendlines (“CPAT”) Cornerstone report posted on November 18, 2025, CPAT has tracked over 115 PE-related transactions from 2020 to 2025, with over 80 transactions in 2025. While PE in the accounting firm space is no longer news, the pace and volume of transactions is certainly news-worthy. Impact of PE Investment The impact of PE investment on the accounting firm space is unprecedented. The APS has enabled PE to fuel billions of capital investment. PE-backed firms provide immediate payouts to partners at appealing valuations while providing access to capital to these firms for merger and acquisition growth, technology investments, and other priorities. Well-capitalized firms now have an improved ability to invest in technological capabilities, attract experienced talent to be more competitive for college graduates, and improve their market position. With new technologies, routine tasks are being automated such as data entry, tie-outs and controls testing, resulting in less time needed to perform certain audit procedures. What the regulators are saying At the AICPA December 2025 conference on Current SEC and PCAOB Developments, common topics were the presence of private equity in the accounting firm space and the opportunities and challenges that come with this investment. PCAOB Acting PCAOB Chair George Botic described that both transformative technologies (e.g., artificial intelligence or “AI”) and the continuing expansion of private equity investments in accounting firms are two developments that bring opportunities and challenges. Mr. Botic noted that while AI has enhanced risk assessment, reduced manual processes and made it possible to efficiently analyze entire populations of data (which can reduce the risk of missing irregularities or unusual patterns), that overreliance on AI may ultimately threaten auditors’ exercise of professional skepticism and judgment. As it relates to private equity, Mr. Botic noted that while these investments have the potential to enhance audit quality by increasing firm capacity and modernizing audit tools with advanced technologies, the presence of private equity presents a risk that firms shift incentives to prioritize profitability over audit quality. Mr. Botic stated, “Both AI and private equity investments in accounting firms carry the potential to truly reshape the profession. Yet these opportunities come with clear challenges to ensure that overreliance on AI and the pressures of private equity do not jeopardize audit quality.” SEC SEC Chair Atkins discussed in his remarks that he would like the PCAOB to modify its inspections process to place more reliance on the system of quality management and that inspection of certain engagements would inform the PCAOB if the firm’s system of quality management is effective. He also expressed a view that accountability for audit quality should move upward to firm leadership. How is a firm’s system of quality management (“SQM”) impacted? Today’s transforming environment has far-reaching impacts on a firm’s SQM. This publication will focus on risk assessment, governance and leadership, ethics and independence, resources, engagement performance, and monitoring and remediation. 
By Jackson Johnson • September 30, 2025
With the effective date for SQMS 1 and QC 1000 fast approaching, firms of all sizes—especially small and sole practitioners—must take action to implement a system of quality management (SQM) that meets the new standards. The good news? You don’t have to start from scratch. Despite QC 1000’s implementation date deferral, the AICPA’s date hasn’t changed, and the international standards are already effective. It’s important to maintain momentum on the efforts toward implementation of all applicable standards for your firm. This article outlines 10 practical steps to help firms build their SQM. Each step includes actionable guidance and considerations for firms with limited resources, and ties into JGA’s broader thought leadership on quality management, risk assessment, and system evaluation. The 10 Steps to Build Your SQM Step 1: Establish a Project Team Form a team with the right mix of quality expertise and operational insight. For small firms, this may mean involving a manager who can grow into a leadership role or setting aside dedicated time as a sole practitioner. Recommended actions to consider: Identify internal champions with interest or experience in quality. Schedule recurring project meetings to maintain momentum. Join a peer group for support and shared learning. Step 2: Understanding and Awareness Document your firm’s business strategy, service offerings, and operational conditions. This step helps identify factors that may impact quality—such as remote work, new industries, or staff turnover. Recommended actions to consider: Conduct a strategy review with firm leadership. List recent changes in firm structure or engagement types. Use these insights to inform your risk assessment. Step 3: Assign Responsibilities Define who is accountable for the SQM. The new standards require clear delineation of ultimate and operational responsibility, including oversight of independence and monitoring. Recommended actions to consider: Assign roles based on existing responsibilities. Clarify delegation boundaries for managing partners. Document responsibilities in your quality manual. Step 4: Establish a Risk Assessment Function Design a process to identify and assess quality risks. This includes understanding conditions or events that could impact quality objectives. Recommended actions to consider: Create a risk assessment policy tailored to your firm. Use relatable examples to demystify risk factors. Leverage AICPA practice aids for structure and templates. Step 5: Perform the Initial Risk Assessment Conduct brainstorming sessions by component and document risks using the AICPA Risk Assessment Template. Include both formal and informal responses. Recommended actions to consider: Use the AICPA risk library to identify common risks. Tailor risks to your firm’s size and services. Include existing responses—even if informal—for evaluation. Step 6: Finalize the Gap Analysis Evaluate where your current responses fall short. This may include undocumented policies or areas where responses don’t fully address the risk. Recommended actions to consider: Identify gaps in governance, ethics, and technology. Determine which informal practices need formalization. Prioritize gaps based on risk severity and regulatory impact. Step 7: Implement Responses to Address the Gaps Develop policies and procedures to close gaps. Responses must be documented and operational. Recommended actions to consider: Draft policies that reflect your firm’s values and risks. Link procedures to specific quality objectives. Use existing documentation as a starting point. Step 8: Update Your Monitoring Process Move beyond peer review prep—monitoring should be continuous and system-wide. Recommended actions to consider: Assign monitoring responsibilities across the team. Incorporate testing of responses into internal inspections. Use dashboards or checklists to track progress. Step 9: Formalize Root Cause and Remediation Procedures Investigate deficiencies and document why they occurred. This step is essential for both system and engagement-level reviews. Recommended actions to consider: Conduct interviews to understand root causes. Use findings to improve policies and training. Apply remediation even if your firm only undergoes engagement reviews. Step 10: Initial Test of Design and Implementation Review documentation and walk through processes to ensure your system is operational and testable. Recommended actions to consider: Validate that each component is supported by evidence. Simulate a peer review to test your system. Confirm that objectives, risks, and responses align. Conclusion Implementing a system of quality management is not just a compliance exercise—it’s an opportunity to strengthen your firm’s foundation for audit quality, risk management, and long-term success. Whether you’re a sole practitioner or a small firm with a few partners, these 10 steps offer a scalable roadmap to meet the new standards. Ready to get started or need help refining your approach? Contact your JGA audit expert today to schedule a consultation and ensure your implementation is tailored to your firm’s needs. At Johnson Global Advisory , we support firms in selecting, implementing, and optimizing these tools to meet their unique needs. For more insights, visit our blog or contact us to learn how we can help your firm AmplifyQuality®.
Show More
September 30, 2026
Overview The September 2026 AICPA Banking Conference highlighted three transformational developments affecting financial institutions: artificial intelligence (AI), digital assets, and regulatory modernization . Collectively, these trends signal a shift toward more technology-enabled banking, increased regulatory clarity around digital assets, and heightened expectations for governance, risk management, and controls. Artificial Intelligence: From Experimentation to Operational Deployment AI is rapidly becoming embedded across banking operations, including fraud detection, Anti-Money Laundering and Know Your Client (AML/KYC) monitoring, predictive analytics, risk management, and audit processes. Regulators and auditors increasingly expect institutions to establish formal governance over AI usage, including controls over data quality, model risk, cybersecurity, explainability, and human oversight. Audit methodologies are also evolving, with greater use of data analytics, continuous monitoring, and full-population testing. Banks that successfully implement AI governance frameworks may achieve operational efficiencies while reducing regulatory and audit risk. Digital Assets: Moving into Mainstream Banking The conference's strongest strategic message was that digital assets should now be viewed as financial infrastructure rather than speculative investments . Stablecoins, tokenized deposits, tokenized securities, and blockchain-based payment rails are increasingly being evaluated by banks as potential sources of growth and competitive advantage. At the same time, these developments create risks related to deposit migration, payment revenue disruption, liquidity management, and regulatory compliance. Regulatory initiatives, including implementation of the GENIUS Act framework and proposed SEC crypto rules, are accelerating institutional adoption and providing greater clarity around permissible activities. Management teams and boards should evaluate how digital assets may impact their business models over the next several years. PCAOB Developments: Greater Focus on Quality Control and Technology The PCAOB continues to make quality control systems a central inspection priority. The amendments to QC 1000 would reduce implementation burdens by eliminating certain requirements, including the External Quality Control Function and fixed September 30 evaluation date, while providing firms more flexibility in assigning responsibilities. Inspection findings remain concentrated in allowance for credit losses (ACL), fair value measurements, investment securities, internal controls, and accounting estimates. Technology, cybersecurity, fraud risk, and AI are becoming increasingly important inspection areas. Public-company banks should expect auditors to devote significant attention to data reliability, management-review controls, and documentation supporting key estimates. SEC Developments: Reduced Compliance Burden and Reporting Reform The SEC's regulatory agenda reflects a broad effort to modernize reporting requirements and facilitate capital formation. Key proposals include optional semiannual reporting, expanded Emerging Growth Company accommodations, filer-status simplification, registered-offering reform, and a proposed framework for crypto-asset offerings. If adopted, these initiatives could significantly reduce reporting and compliance costs for many public banking organizations while expanding access to scaled disclosure accommodations. Banks should continue monitoring these proposals, as they could materially affect reporting obligations, internal controls, and capital markets activities. Boards and management should prioritize: Establishing formal AI governance and risk-management frameworks. Evaluating strategic opportunities and risks associated with stablecoins and tokenized financial assets. Preparing for increased auditor and regulator focus on ACL, estimates, data quality, and internal controls. Monitoring SEC reporting reforms and potential compliance-relief opportunities. Assessing how technology investments can improve efficiency while strengthening governance and risk management. Conclusion The conference signaled that the banking industry is entering a new phase in which AI adoption, digital asset integration, and regulatory modernization are becoming mainstream strategic priorities. Audit firms will need to adapt their methodologies, quality control systems, technology governance, and staff capabilities to address these developments effectively. Our JGA experts can help assess emerging risks, strengthen quality-control and audit methodologies, enhance documentation and inspection readiness, and implement practical approaches for auditing AI-enabled processes, digital assets, complex estimates, and internal controls.
September 22, 2026
At Johnson Global Advisory, we believe in making a meaningful difference beyond our profession. We are proud to support Compassion International and its mission to help children overcome poverty through education, healthcare, life-changing resources, and hope. Through this contribution, we are investing in brighter futures for children, families, and communities around the world. We invite others to join us in supporting organizations like Compassion that are creating lasting change and transforming lives one child at a time.
September 10, 2026
In our previous alert, Open Board Meeting: PCAOB to Consider Adopting New Standards on General Responsibilities of the Auditor in Conducting an Audit, Quality Contro l, we discussed the PCAOB's plans to consider amendments to QC 1000 and related quality control reporting requirements. At its September 9, 2026 Open Meeting , the PCAOB adopted a series of amendments to QC 1000 and related reporting requirements designed to improve scalability, reduce implementation burden, and further align certain aspects of the standard with other quality management frameworks. While the amendments provide meaningful changes in several areas, firms remain responsible for establishing and maintaining an effective system of quality control starting December 15, 2026. The following table summarizes the key amendments adopted by the Board and JGA's insights regarding the implications for registered firms.
Show More